Set Authentication
Open in CMSWhen several APIs share the same credentials, for example all the actions you imported from one OpenAPI schema, you can configure authentication once and apply it to all of them in a single step. This tutorial walks you through Set authentication on the Custom API page, using the project APIs of Atlas, Kirana Group's operations assistant.
Before you start
- You have at least one API on the Custom API page, either added by hand (Connect Your API) or from a spec (Import an OpenAPI Schema). Atlas has
get_project_statusandlist_projects. - You have the credentials for those APIs: a token, a username and password, a custom header key, or OAuth details.
- You know how to test and publish changes. See Preview and Publish Changes.
About the sample API: the Kirana Projects API used in these tutorials is a public sample and does not accept credentials. If you send it a Bearer token, it answers
403. Kirana's real Projects API would require a Bearer token, which is the situation this page describes. If you follow along with the sample, click Cancel at the end of Step 3 instead of Apply to N APIs, or set the APIs back to None afterwards.
When to Use This Feature
Use Set authentication when:
- You have just imported multiple APIs from an OpenAPI schema and need to add credentials to all of them at once
- Several existing APIs on your agent use the same token or username and password, and you need to rotate or update that credential
- You want to apply or remove authentication on a specific set of APIs without editing each one individually
Supported Authentication Types
| Authentication type | When to use |
|---|---|
| None | Public endpoints, no credentials needed. Also removes existing authentication. |
| Basic | APIs that use a username and password |
| Bearer | APIs secured with a static Bearer token |
| Custom | APIs with a custom header name (for example X-API-Key) |
| Oauth | APIs secured with OAuth 2.0 (Client Credentials or Google Service Account) |
Step 1: Open Set authentication
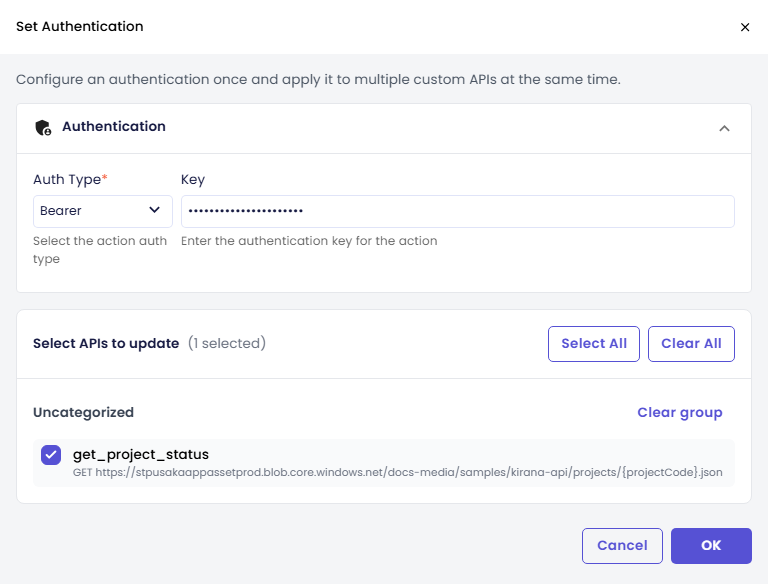
On the Custom API page, open More actions and click Set authentication. The Set authentication drawer opens with the line "Set the authentication once and apply it to several custom APIs. It replaces what each of them has now."
Step 2: Configure the Authentication
In the Authentication section, choose the Authentication type that matches your API. The fields for that type appear next to it. For Kirana's Projects API, choose Bearer and paste the token into Token. The value is masked as you type.
| Authentication type | Fields to fill in |
|---|---|
| Bearer | Token: the token value |
| Basic | Username and Password |
| Custom | Header name (for example X-API-Key) and Key. qlar sends Header name: Key with every request. |
| Oauth | OAuth provider (Client Credentials or Google Service Account), Token URL, and the provider's credentials. See Authentication Details Reference. |
| None | No fields. Use it to remove authentication from the selected APIs. |
Step 3: Select the APIs and Apply
Under APIs to update, tick the APIs that should get this authentication. APIs are grouped by category; APIs without a category are under Uncategorized. The header shows how many are selected, for example 1 of 3 selected.
- Select all ticks every API in the list.
- Clear all unticks every API.
- The checkbox on a category header ticks or unticks all APIs in that category. Use Search APIs to find one by name.
In the screenshot, get_project_status is ticked. For Atlas, tick list_projects as well, since both call the same API.
Click Apply to N APIs, where N follows your selection. It is off until at least one API is ticked. A confirmation asks Replace authentication?, says how many APIs lose their current authentication, and warns that the page's other changes are saved too. Click Yes.
Note: This overwrites the existing authentication on every selected API. APIs you do not select are left untouched.
Step 4: Confirm the Save
Clicking Yes saves the new authentication straight away, so you do not need Save all changes. The CMS confirms Custom APIs saved.
The updated authentication is saved as a draft. It reaches real users after you click Publish in the top bar.
Check the result
- In the list, the chip next to each updated API now shows the new auth type, for example Bearer instead of None.
- Click one of the updated APIs, then Test API. The API section shows the new Authentication. Fill in a sample value, for example
KG-2041, and click Call API. A401or403status usually means the credentials are wrong, or, with the public sample, that the API does not accept credentials at all. - In the preview panel, ask a question that should trigger one of the updated APIs, for example "What is the status of KG-2041?", and confirm that Atlas answers with real data.
- Click Publish when everything works. See Preview and Publish Changes.
Authentication Details Reference
Bearer token
| Field | Description |
|---|---|
| Key | The full token value (without the Bearer prefix; qlar adds it automatically) |
Basic authentication
| Field | Description |
|---|---|
| Username | The account username |
| Password | The account password |
Custom header
| Field | Description |
|---|---|
| Header name | The HTTP header name your API expects (for example X-API-Key or Authorization) |
| Key | The value sent in that header |
OAuth 2.0, Client Credentials
| Field | Description |
|---|---|
| Token URL | The endpoint qlar calls to obtain an access token |
| Client ID | Your OAuth client identifier |
| Client secret | Your OAuth client secret |
| Scopes | OAuth scopes your API needs (optional). Type each scope and press Enter. |
OAuth 2.0, Google Service Account
| Field | Description |
|---|---|
| Token URL | Filled in for you (https://oauth2.googleapis.com/token) |
| Google Service Account JSON | The key file of your service account from Google Cloud Console |
| API Scopes | The Google API scopes the token should cover |
| User Delegation (Optional) | The email of the user to impersonate. Required for Gmail APIs, optional for Calendar APIs. |
Next steps
- Next in the journey: Connect an MCP Server, to give your agent many tools from one server connection.
- Connect Your API: configure authentication for a single API action.
- Using Plugins: use pre-built integrations that handle authentication for you.